Case Study

eGovernment API Development

Mala'a, Sultanate of Oman
innovation-image

Overview

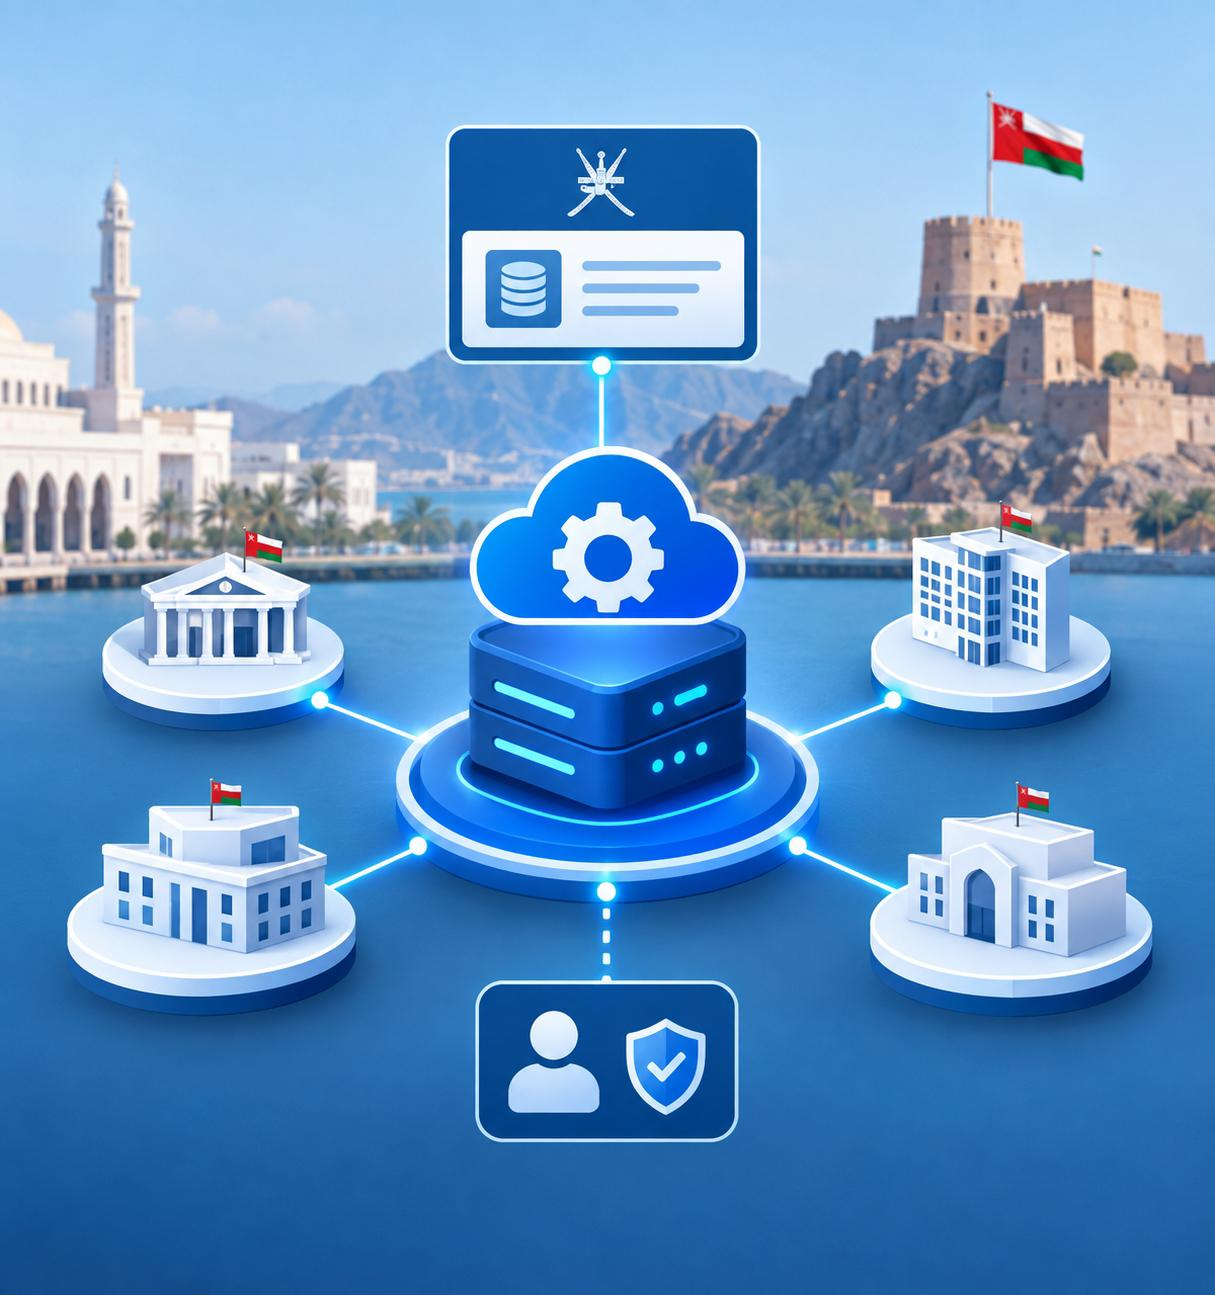
Mala'a required a secure Electronic Government API Platform to enable authorized government entities within the MPLS network to access selected data based on their assigned roles and approved permissions.

The platform was designed to provide controlled and configurable access to information while ensuring that each user or entity could retrieve only the data fields specifically authorized for them.
Business Need

The solution needed to provide government entities with a secure and standardized method to request and retrieve data from Mala'a through APIs.
A key requirement was to ensure field-level access control, where Mala'a administrators could define which data fields were available from different data sources and determine which fields each role was permitted to access.
The list of available and authorized fields also needed to be fully configurable, allowing Mala'a to manage access rules without requiring application code changes.

Solutions

GulfCyberTech designed and implemented a secure API platform within Mala'a's environment using a three-tier architecture.
The platform enables authorized government entities within the MPLS network to retrieve data according to predefined roles and field-level permissions. Administrative users can configure available data fields, manage authorization rules, and control what information is exposed through the APIs.
The solution was developed with strong security controls, auditability, and centralized configuration to ensure that access to information remains controlled and traceable.

Security & Compliance

The platform was subjected to security testing, vulnerability assessment, and penetration testing before production deployment.
All identified findings were addressed in line with Mala'a's information security requirements before the system was approved for go-live.

Key Highlights

  • Secure API access for authorized government entities.
  • MPLS-based controlled connectivity.
  • Role-based and field-level data authorization.
  • Configurable data-field management.
  • Integration with multiple approved data sources.
  • Three-tier application architecture.
  • Centralized access and permission management.
  • Comprehensive audit and activity logging.
  • Vulnerability assessment and penetration testing.
  • Complete source-code and technical-documentation handover.

Result

The platform was successfully implemented and deployed within Mala'a's environment within the planned project timeframe.
It provides a secure, configurable, and controlled mechanism for government entities to access authorized information while giving Mala'a full control over data exposure, user roles, and field-level permissions.
system-image